CVE-2026-122125 — ICRTouch ByTable and TouchTakeaway do not consistently implement anti-CSRF protections for state-changing web requests. The affected functio
ThreatFilter threatfilter.dev
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.(vendor/severity tags below are heuristic) ICRTouch ByTable and TouchTakeaway do not consistently implement anti-CSRF protections for state-changing web requests. The affected functionality does not require a per-session CSRF token or otherwise verify that requests originated from an authorized application context. An attacker who convinces an authenticated user to visit a malicious website may cause the user’s browser to submit unauthorized requests to the platform using the user’s active session.
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
 2026 United States elections
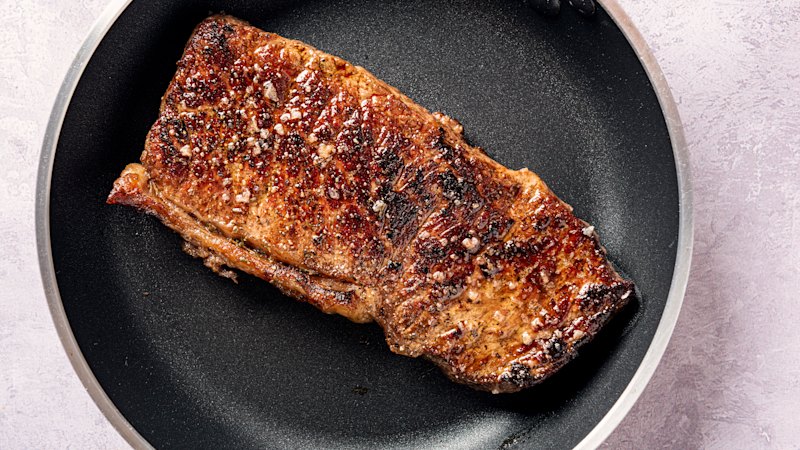 I had to wait 30 years for my aunty to drop this game-changing cooking hack
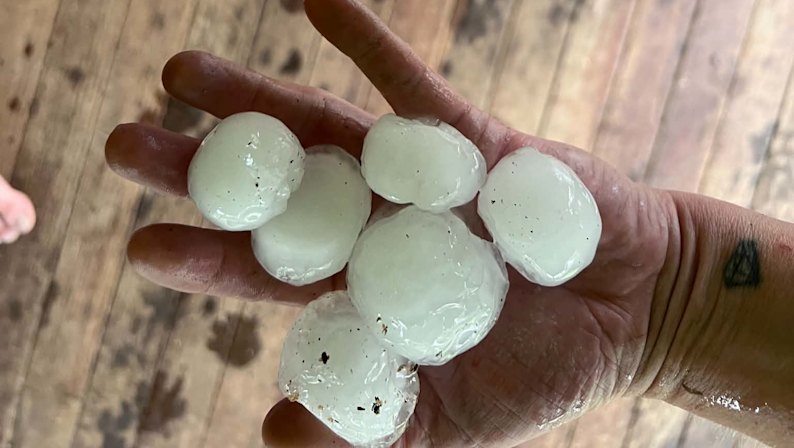 Giant hail and destructive winds: Storms hit Brisbane and state’s south-east