Security Boulevard: Attackers Can’t Steal Passkeys, So They’re Enrolling Their Own
FIDO CTAP fidoalliance.org
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.*** This is a Security Bloggers Network syndicated blog from Deepak Gupta’s notebook authored by the team. Read the original post at: https://guptadeepak.com/passkey-enrollment-attacks/
Passkeys cannot be phished the way passwords can, so attackers have changed targets. A vishing campaign documented by Okta Threat Intelligence talks employees through a fake Microsoft Entra sign-in page. Meanwhile, the attacker uses what the victim types to sign in to the real account and register a passkey of their own. The weak point is no longer sign-in. It is enrollment and recovery.
More ways to use this
Open on another device
Scan to open this page. Your saved notes and account access are not included.
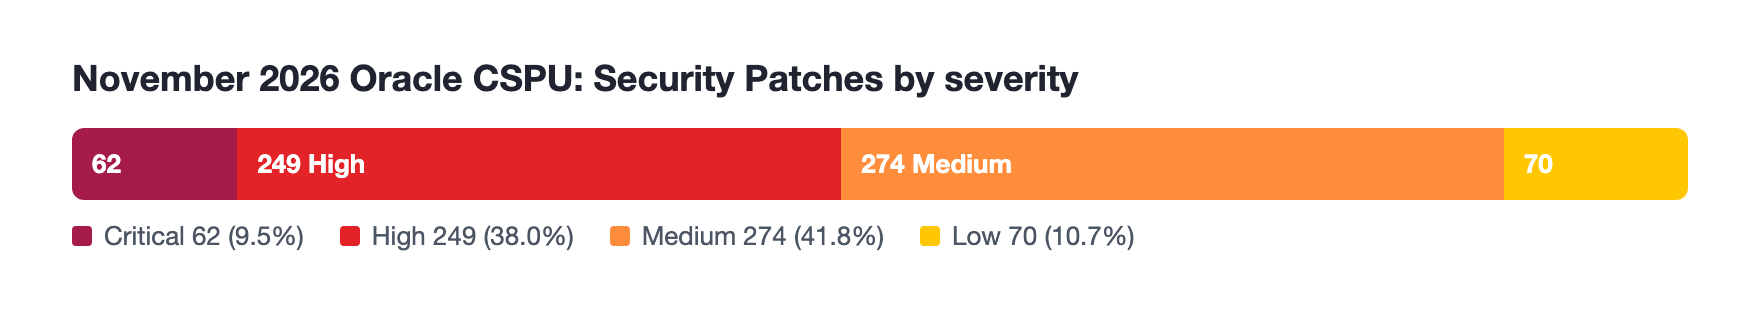 Oracle November 2026 Critical Security Patch Update Addresses 640 CVEs (CVE-2026-114938)