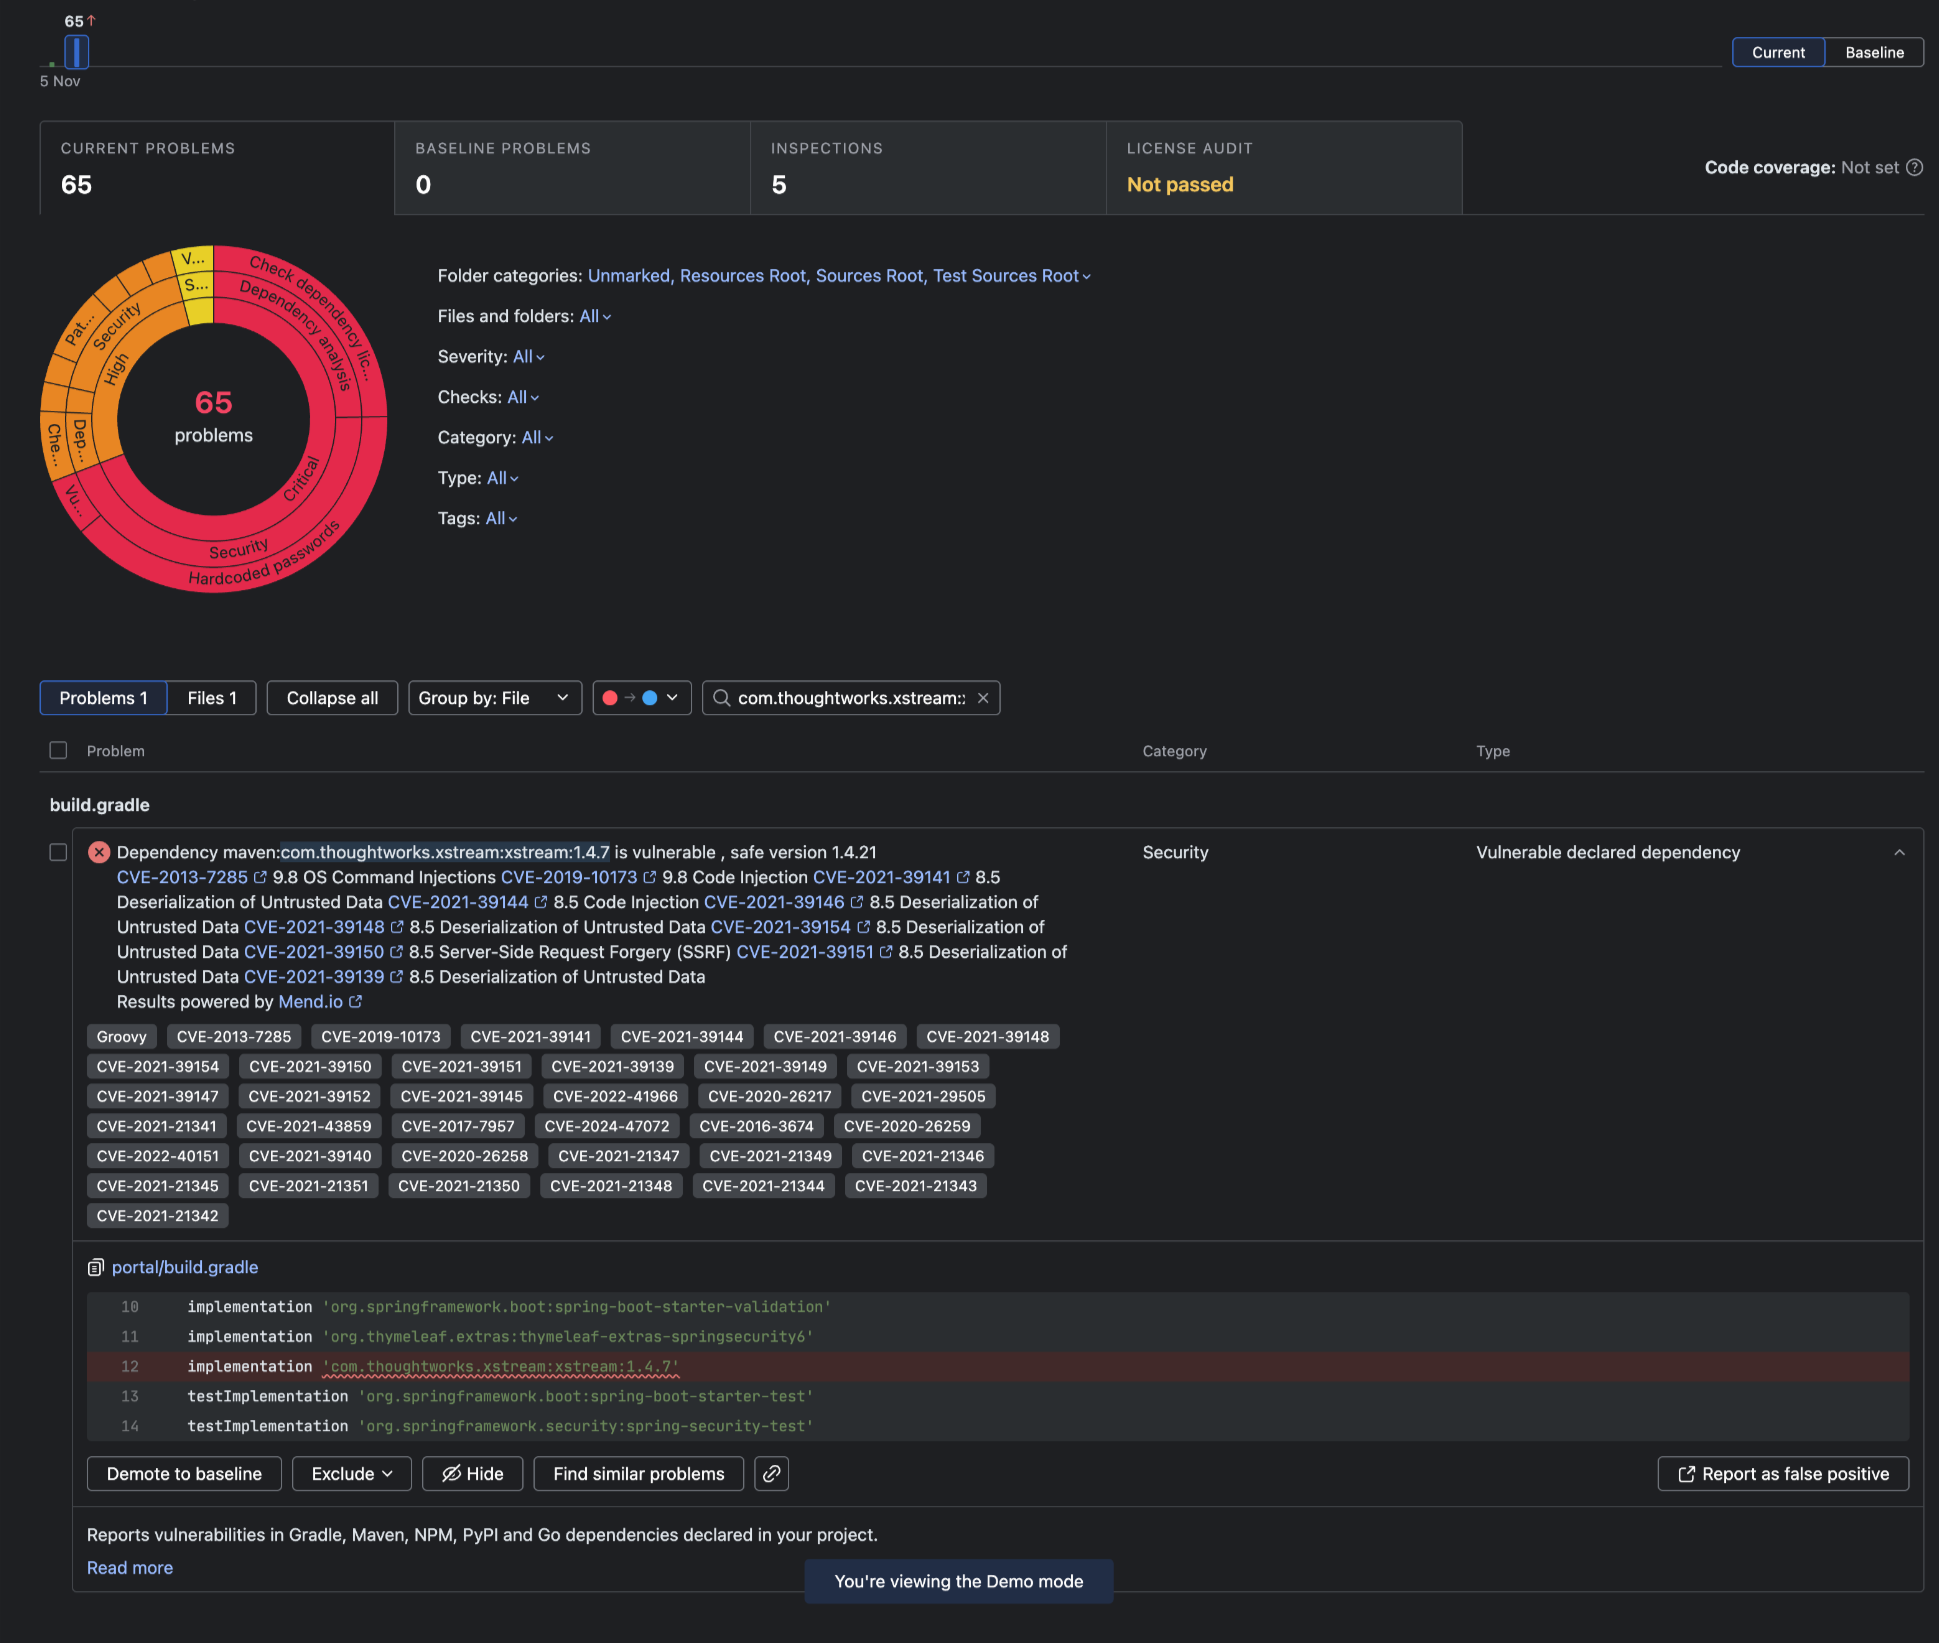
AI-Generated Code Security Risks: What Qodana Found in a Java App
JetBrains Blog jetbrains.com
Listen to this summary
Adding search functionality, converting a document, or connecting a service sound like small changes. An AI coding agent may take it on in one pass, changing application logic, dependencies, configuration, and tests along the way. The result may pass functional tests and still contain security vulnerabilities.
Static analysis can surface some AI-generated code security risks, while reviewers and targeted tests determine which findings matter in practice. Where can external input travel? What happens if a configuration value is missing? Do the new dependencies introduce risks the functional tests never exercise? The same questions matter in any codebase, including code written with AI.
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
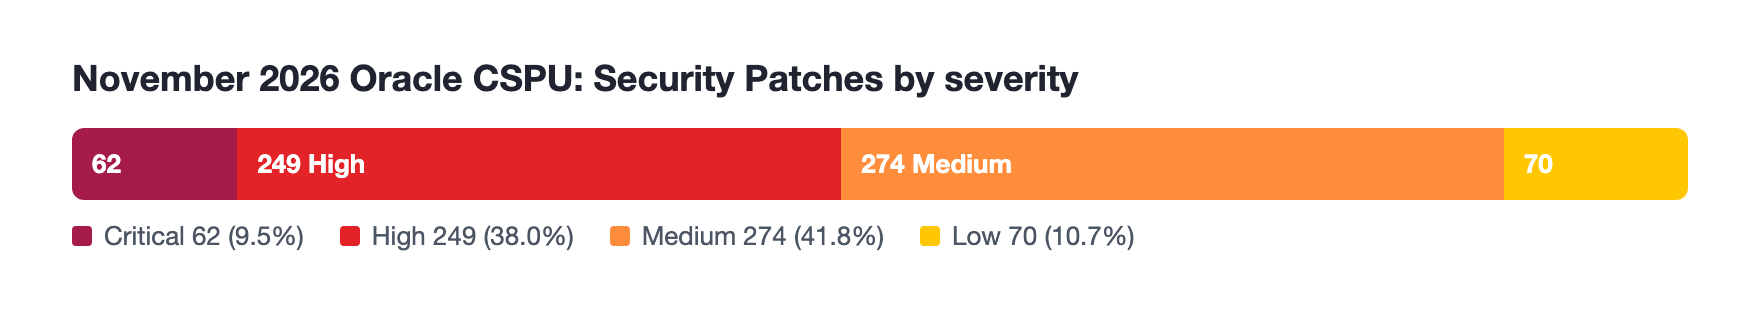 Oracle November 2026 Critical Security Patch Update Addresses 640 CVEs (CVE-2026-114938)